Agentic AI governance fails when it borrows its controls from the chatbot era. Nearly every AI control organizations have built so far, the acceptable-use policy, the training module, the prompt review, assumes a human at the keyboard reading what the model says before anything happens. Agents break that assumption. They do not just answer; they act. They issue tool calls, send requests, and touch systems on their own, at machine speed, often overnight. Governing them means moving the control point to the moment a request leaves the device for a governed provider, whoever or whatever initiated it.
Your current controls govern people, not software
Look at the AI controls most organizations stood up over the past two years and ask who each one actually governs. An acceptable-use policy governs a person’s choices. Training governs a person’s habits. Prompt review governs what a person is about to send. Each works, to a point, because a human pauses before the next step and can be taught, persuaded, or stopped.
An agent does none of that. It cannot read the policy, will not attend the training, and never pauses for review. Ask one to reconcile a spreadsheet and it may fetch records, query systems, draft messages, and retry failures in a loop, each step a real request leaving a real device. The OWASP GenAI Security Project’s work on agentic threats catalogs what can follow: tool misuse, injected instructions that redirect an agent mid-task, data leaking through steps no one designed. None of those failure modes involves a person breaking a rule. The software did what software does.
| Control | What it governs | What an agent does with it |
|---|---|---|
| Acceptable-use policy | A person’s choices | Never reads it |
| Training | A person’s habits | Cannot attend |
| Prompt review | Text a person is about to send | Sends without asking |
| Policy at the action boundary | The request itself | Governed the same way, on a governed provider |
What changes when the model acts
Speed and volume change first. A person sends a prompt every few minutes and reads the answer. An agent can issue hundreds of requests an hour and keep working while the building is empty. Any control that depends on someone noticing a problem in the moment stops working, because there is no moment and no one watching.
Initiative changes second. The prompt you approved is not the action the agent takes. A single instruction fans out into tool calls no one reviewed, against systems no one named. Reviewing what the model says and governing what it does are now two different jobs, and most organizations have only staffed the first.
Arrival changes last. Agents spread the way shadow AI did: through individual staff, inside products that quietly added them, ahead of any procurement decision. If unapproved chat tools reached your fleet before your policy did (our explainer on what shadow AI is covers how), assume agents already have. AI agent risk belongs on the agency risk register now, because it is software acting with a person’s access, minus the person.
Agentic AI security starts at the action boundary
There is one place these actions can be governed: the boundary where a request leaves the device for a provider. Not the model, which you do not control. Not the person, who may not be present. The action itself, at the moment it happens.
A decision made at that boundary has properties nothing upstream can match. It sees the request as it is actually sent, not as the prompt described it. It can act, ALLOW, BLOCK, or REDACT, before the action runs rather than after. And it is indifferent to who initiated the request. The same policy holds for a person pasting a patient record into a chat window and an agent sending that record inside a tool call at three in the morning. That indifference is the point. You do not need a second governance program for agents. You need one policy that governs actions, applied to every actor whose traffic reaches a governed provider.
A fair test for any control you are evaluating: does it produce the same decision for a person pasting a record and an agent sending one? If the answer depends on who is at the keyboard, it governs people, not actions.
With agents, evidence matters more, not less
When a person misuses a chat tool, there is at least a person to ask. When an agent acts overnight, no one watched it happen, and the signed record is the witness you can hold. For every captured interaction it shows what was sent, what was decided, and what crossed.
For public agencies this is not a new obligation, only a sharper one. NIST SP 800-53 rev 5 dedicates the AU family to audit and accountability, including AU-10 on non-repudiation, and CJIS Security Policy v6.1 maps to those controls, with its remaining priority levels fully auditable by October 1, 2027. What agents change is what the record must survive. Evidence of an autonomous action will be challenged: was this entry altered, and who sent it? A log an administrator can edit answers none of that. The bar is a record signed where the action happened, hash-chained so any change is visible, and held by the agency, not the provider. Tamper-evident, with the user and device identity the checkpoint reports, for every captured interaction.
Where federal direction points
On June 2, 2026, the White House issued an Executive Order titled “Promoting Advanced Artificial Intelligence Innovation and Security”. It directs work on AI-enabled cyber defense and a voluntary framework for frontier models, with detail expected later in 2026. It does not yet tell a hospital or a police department how to govern AI agents, and it would be a mistake to read specific requirements into it today. The direction, though, matches everything above: organizations will be expected to control what AI systems do and to hold evidence that the controls held. Control the action, hold the evidence. Programs built on that footing will not need rebuilding when the detail lands.
How Verillian governs the action
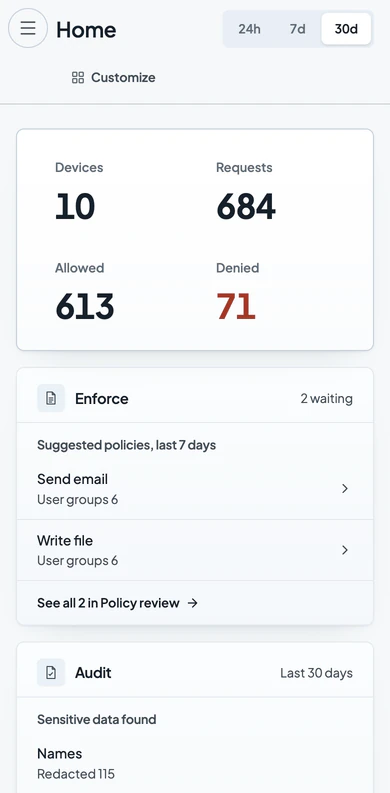
Verillian is built on this position. Governance, in most organizations, is a meeting. Enforcement is what Verillian does. A checkpoint on each device covers the AI tools and agents that reach a service Verillian inspects, with no per-tool integration, and applies your policy at the moment of execution, person or agent alike. Every captured interaction is signed on the device and hash-chained into a tamper-evident record your agency holds on a server the agency runs; Verillian hosts nothing. How it works is on the platform page, and how it anchors an agency’s AI governance program is at adopt AI within your mandate. The model proposes. Verillian decides.