Two layers apply together, and neither one by itself is the full answer. The CJIS Security Policy’s audit and accountability controls set a general floor for any system that touches criminal justice information, AI tools included, with no provision written for AI tools. California then adds report-specific audit trail fields for AI-assisted report writing, and Utah adds a disclaimer and the author’s certification instead. Read together, a California department needs both sets of fields covered, and the California fields kept as long as the official report is kept, which is a different clock from CJIS’s.
What does CJIS require in general, and what does it not require?
Nothing in the CJIS Security Policy, version 6.1, is written for AI tools or requires an “AI audit log”; its one mention of artificial intelligence is in a malware-detection discussion. What it requires is narrower and older: it applies to all entities with access to criminal justice information, or that operate systems used to process, store, or transmit it, and its Audit and Accountability, AU, control family applies to such a system the same way it applies to any other system that handles CJI. An AI report-writing tool that receives CJI is such a system. The AU family, and the five questions it reduces to when the system is an AI tool, are covered in full in what the CJIS Security Policy requires before AI touches CJI, and this page will not repeat that ground. The short version worth carrying forward: CJIS sets a generic floor for controlling and auditing access to CJI. It does not know or care that the access happened through an AI tool.
What do California and Utah require specifically for AI-drafted reports?
California’s Penal Code section 13663 adds fields CJIS never asked for: the audit trail must identify the person who used AI to create the report, and the video and audio footage used, if any. Utah Code section 53-25-902 takes a different path entirely and requires an agency AI-use policy, a disclaimer in the report and the author’s certification rather than an audit trail at all. The full comparison, statute by statute, is worked through in what has to be preserved when an officer uses AI to draft a report, including the table of what each state requires and what neither one does. This page picks up where that comparison leaves off: what the combined record actually has to contain and hold onto, once both layers are stacked.
How long does the audit trail actually have to survive?
Two different clocks run at once. The CJIS Security Policy’s control AU-11, which uses the numbering of NIST SP 800-53’s Audit and Accountability family, says to “retain audit records for a minimum of one (1) year or until it is determined they are no longer needed for administrative, legal, audit, or other operational purposes,” a floor already covered in what an AI audit trail actually contains. California’s statute runs on a different clock entirely: the AI’s first draft and the audit trail must be kept for as long as the official report itself is retained, and the department’s own records-retention schedule, not CJIS, decides how long that is. That period is set state by state and department by department, so this page does not state one. Utah imposes no retention duty on the draft at all.
The practical rule follows from stacking the two: if one audit trail is meant to answer both, it has to survive as long as the longer clock requires. A retention schedule written only to CJIS’s one-year minimum falls short of California’s statute wherever the department keeps its official reports longer than a year.
What fields does a defensible audit trail actually contain?
Combine the two layers and the field list is short enough to check against directly:
- Who used the tool. A specific person, per California’s requirement that the audit trail identify the person who used AI, and CJIS’s requirements that users be uniquely identified (IA-2) and that audit records establish the identity of the individuals associated with each event (AU-3).
- What happened, and when. The CJIS baseline: audit records that establish the type of event, when and where it occurred, its source and its outcome (AU-3), with time stamps from the system clock (AU-8).
- Which footage or recording the tool drew on, if any. California’s addition, not required by CJIS at all.
- Whether the record is protected from silent alteration. CJIS control AU-9 requires audit information to be protected from unauthorized access, modification, and deletion, whatever fields the record captures.
- Retained on the longer of the clocks that apply to your agency, not the shorter one.
A real, currently posted example shows what one department added on top of that list once it started vetting AI systems rather than only writing a use policy. Fargo, North Dakota’s police department policy has its AI coordinator weigh “accountability and transparency,” defined as “the ability to track and measure the system’s use and activity through histories, audit logs, and other processes,” as one of seven characteristics balanced before recommending a GenAI system to the Chief of Police for approval. That is a procurement question, whether the vendor’s tool can produce this kind of record, asked before deployment, which is a different moment from the audit questions above, asked after the fact about a specific use.
Who actually checks whether the audit trail meets these requirements?
For the CJIS layer, the policy answers it: the state’s CJIS Systems Agency completes a triennial audit of the agencies with access to CJIS systems through it, and the FBI’s CJIS Audit Unit audits the CJIS Systems Agencies, an audit of agencies rather than a certification of any product. For the state-specific layer, it is not settled the same way. Neither California’s nor Utah’s statute names a regulator or an auditor who checks compliance with the report-specific requirements, and neither sets up a routine audit of them the way CJIS does. Until a statute or regulation names one, where compliance gets tested is left to the department’s own supervision and, in a particular case, to counsel and the court. What a missing draft or audit trail means in a case is a discovery question, covered in is an AI-generated police report discoverable, which this page will not repeat.
CJIS sets a floor that already reaches AI, with no AI-specific rule needed. California adds report-specific audit trail fields and Utah adds report-specific disclosures, on top of that floor, not in place of it. A department meeting only the shorter of the retention clocks, or only the CJIS floor and not the state-specific requirements, has not met both.
Sources
- CJIS Security Policy, version 6.1, June 25, 2026, FBI Criminal Justice Information Services Division. Full policy text, read September 26, 2026.
- California Penal Code section 13663, added by SB 524 (2025 to 2026 Regular Session). Chaptered bill text, read September 26, 2026.
- Utah Code sections 53-25-901 and 53-25-902, enacted by SB 180 (2025 General Session). Current code section, read September 26, 2026.
- NIST SP 800-53, revision 5, Audit and Accountability control family. Full publication, read September 26, 2026.
- Fargo Police Department, Policy 345, Generative Artificial Intelligence Use, original issue August 12, 2025. Full policy text, read September 26, 2026.
Where Verillian fits
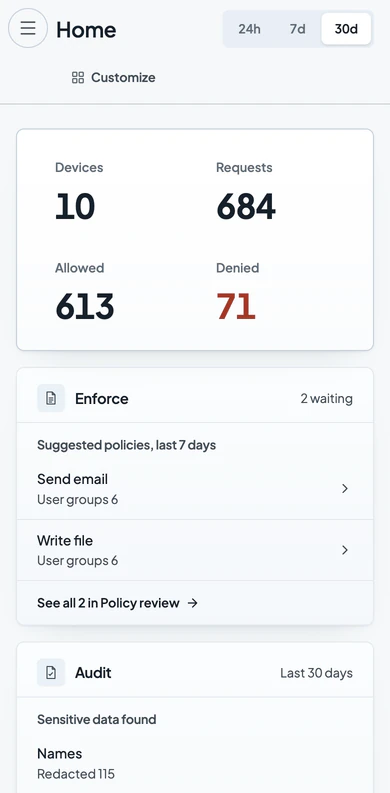
Verillian governs AI use on the devices you enroll. A checkpoint on each device sits between your people’s AI tools and agents and the AI providers. A tool call your policy bans is removed before your machine can run it. Each record is signed on the device it came from and hash-chained to the one before it, so a change to its signed fields is detectable, and it stays on your own infrastructure. The admin server runs where you choose: on premises or in a private cloud you run. macOS, Windows and Linux are supported. For a department, each entry is attributed to the user and device the checkpoint reports, with the time, for use that starts on an enrolled device, one of the fields both layers above ask for.
When a vendor’s service calls a model on the vendor’s servers, as an ambient scribe or a hosted report-writing tool does, the record of what that model received is created on the vendor’s side, and the contract is your lever for it. What Verillian gives you is the record of AI use that starts on your own devices.
Our compliance mappings show the controls the platform supports, the audit trail page shows what a device-side record contains, and the public safety section of the site covers what this looks like for an agency already running AI tools day to day.