NIST SP 800-171 audit logging for AI use, and CMMC Level 2.
Verillian applies your AI policy on your staff’s devices and keeps the record on your own servers.
Do the audit requirements cover staff AI use?
CMMC Level 2 uses the 110 NIST SP 800-171 R2 requirements as written (32 CFR Part 170). Requirement 3.3.1 asks for audit logs “to enable the monitoring, analysis, investigation, and reporting of unlawful or unauthorized system activity”. Requirement 3.3.2 asks that “the actions of individual system users can be uniquely traced to those users”. When staff use AI tools on a covered system, that trace exists only if you keep it.
What do CMMC and NIST SP 800-171 ask, one by one?
Audit logs that trace each action to one user, alert when logging fails, carry synchronized time stamps and are protected from change. CMMC Level 2 uses the NIST SP 800-171 requirements as written.
The requirements’ words are on the left, and what a Verillian record shows is on the right.
Sources: eCFR, current as of October 6, 2026, for 32 CFR Part 170 and 48 CFR 252.204-7012; NIST SP 800-171 Revision 2 (February 2020, includes updates as of January 28, 2021) on nvlpubs.nist.gov; and NIST’s publication page for it. All read on October 8, 2026: 32 CFR 170.4, 32 CFR 170.14, 32 CFR 170.17, 48 CFR 252.204-7012, NIST SP 800-171 Rev 2 (PDF), NIST publication page. Every quotation comes from them.
This is not legal advice or an assessment opinion.
| What the requirement asks | A Verillian record shows |
|---|---|
| ‘The security requirements in CMMC Level 2 are identical to the requirements in NIST SP 800-171 R2.’ The rule counts ‘the 110 Level 2 requirements from NIST SP 800-171 R2’. To reach a Level 2 (C3PAO) status the organization must ‘complete and achieve a MET result for all security requirements’ and ‘obtain a Level 2 certification assessment from an authorized or accredited C3PAO’. 32 CFR 170.14(c)(3), 170.4, 170.17(a)(1) | Entries for AI use on enrolled devices, which a reviewer reads in the console, on your own servers. They bear on the Audit and Accountability requirements below. |
| 3.3.1 ‘Create and retain system audit logs and records to the extent needed to enable the monitoring, analysis, investigation, and reporting of unlawful or unauthorized system activity.’ NIST SP 800-171 Rev 2 | One entry for each captured AI request from an enrolled device to an AI provider on your signed policy’s list, with the time and the decision (allowed, redacted or denied). |
| 3.3.2 ‘Ensure that the actions of individual system users can be uniquely traced to those users, so they can be held accountable for their actions.’ NIST SP 800-171 Rev 2 | The user and device as the device reports them, on an entry that the device signs. |
| 3.3.3 ‘Review and update logged events.’ NIST SP 800-171 Rev 2 | Entries that a reviewer can search by decision and AI provider in the console. |
| 3.3.4 ‘Alert in the event of an audit logging process failure.’ NIST SP 800-171 Rev 2 | When a device’s records stop being saved, or stop reaching your servers, it raises a critical alert. |
| 3.3.5 ‘Correlate audit record review, analysis, and reporting processes for investigation and response to indications of unlawful, unauthorized, suspicious, or unusual activity.’ NIST SP 800-171 Rev 2 | Entries that a reviewer reads and exports from the console. |
| 3.3.6 ‘Provide audit record reduction and report generation to support on-demand analysis and reporting.’ NIST SP 800-171 Rev 2 | Search and export of entries in the console, using the metadata it indexes: user, device, provider, model and decision. |
| 3.3.7 ‘Provide a system capability that compares and synchronizes internal system clocks with an authoritative source to generate time stamps for audit records.’ NIST SP 800-171 Rev 2 | The time stamped on each entry. |
| 3.3.8 ‘Protect audit information and audit logging tools from unauthorized access, modification, and deletion.’ NIST SP 800-171 Rev 2 | The device signs every entry, and your own servers flag any entry that fails to verify when it arrives. Change a signed field later and the check shows it. Content is encrypted to your organization’s own key, which your administrator creates in the browser. Verillian never receives that key. |
| 3.3.9 ‘Limit management of audit logging functionality to a subset of privileged users.’ NIST SP 800-171 Rev 2 | Sign-in to the console runs through your own identity provider, and an administrator assigns roles in the console. |
| Clause 252.204-7012 (MAY 2024) makes the covered contractor information system ‘subject to the security requirements in National Institute of Standards and Technology (NIST) Special Publication (SP) 800-171’ as ‘in effect at the time the solicitation is issued or as authorized by the Contracting Officer’. Subcontracts are covered too: include the clause where ‘subcontract performance will involve covered defense information’. 48 CFR 252.204-7012(b)(2)(i), (m)(1) | Each organization keeps the entries from its enrolled devices on its own servers. |
Who decides if your AI use meets the requirements?
Your C3PAO and your counsel decide. Final Level 2 (C3PAO) status needs a MET result for every security requirement in an assessment by an authorized or accredited C3PAO (32 CFR 170.17(a)(1)). Verillian gives your assessor a record to read.
How does each AI request trace to one user?
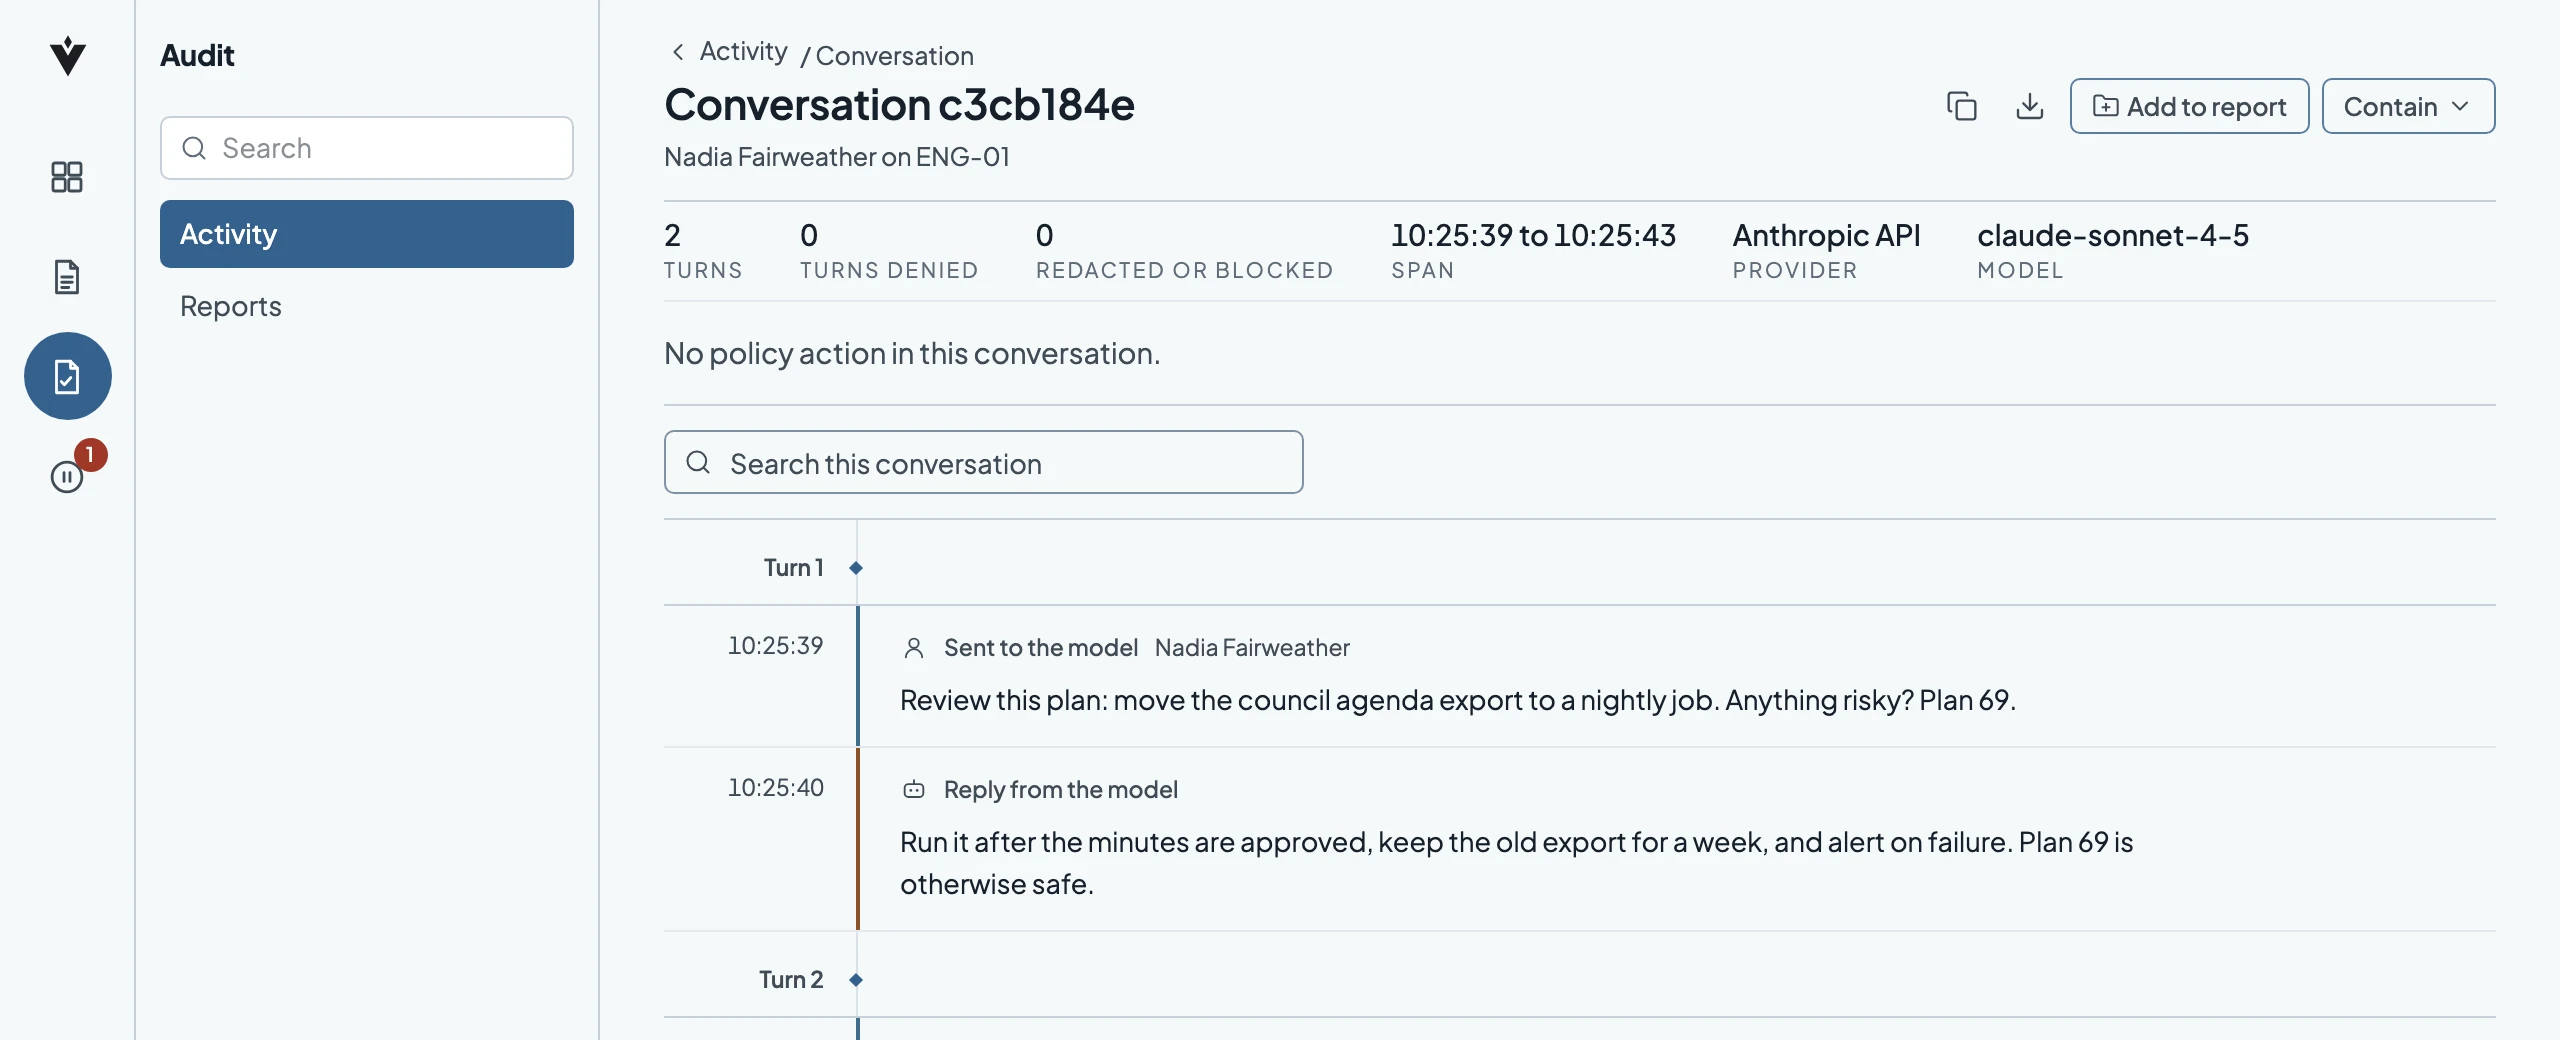
Each captured request becomes one entry with the time, the decision, the user and the device, signed on the device. Your own servers flag any entry that fails to verify, and the record is immutable: it can’t be quietly edited afterwards. That’s an AI audit trail.
What can you hand your assessor?
Requirement 3.3.6 asks for “audit record reduction and report generation to support on-demand analysis and reporting”. Search the record by user, device, provider, model and decision, then export the matching records, and the export goes on the record under the reviewer’s name. Requirement 3.3.9 limits who manages audit logging to a subset of privileged users. Sign-in to the console runs through your own identity provider, and an administrator assigns the roles. The Defense Overview and the Security Packet open with no form.
What evidence of AI use will an assessor want?
All posts
See how Verillian keeps CUI out of public AI.