AI policy enforcement, decided on your own devices.
Verillian enforces your AI policy on each enrolled device, deciding what an AI tool or agent may do before a prompt leaves or a command runs, and keeping the record on your own infrastructure.
AI that acts needs a decision before it runs
- A checkpoint on each device
- Rules for which tools may run
- Sensitive data redacted before it leaves
- Every captured interaction recorded
- Signed under your own key, on your own infrastructure
- Search and export for records requests
- Cut off a provider for everyone
- Org-wide switch
- Reverse in one action
Built and live. Installed with a Verillian engineer, on your own infrastructure.
Redaction is best effort.
Read this diagram as text
Three jobs, one path. Govern: a checkpoint on each device, rules for which tools may run, and sensitive data redacted before it leaves. Audit: every captured interaction recorded, signed under your own key on your own infrastructure, with search and export for records requests. Contain: cut off a provider for everyone, an org-wide switch, and reversal in one action. Built and live, installed with a Verillian engineer on your own infrastructure.
Three jobs of AI governance, one page each
How on-device AI policy enforcement runs
| Part | What it does |
|---|---|
| Where it decides | On each enrolled device, before a prompt leaves or a command runs. Nothing to train, and no intent model in the path. |
| Decisions | Allow, redact, block or log. Under the same policy, the same request draws the same decision every time. |
| Rules | Per tool and per group. The strongest setup is an allow list: name what the work needs, and anything else is refused. |
| Policy changes | Every change carries a justification, takes effect as written, and the policy version rides with each decision. |
| The record | Each captured request is hash-chained, signed and encrypted to your key, so a change to its signed fields is detectable. |
| Containment | Cut off one provider for everyone, or stop AI across the fleet with one typed confirmation. Bringing it back is as fast, and both land in the record. |
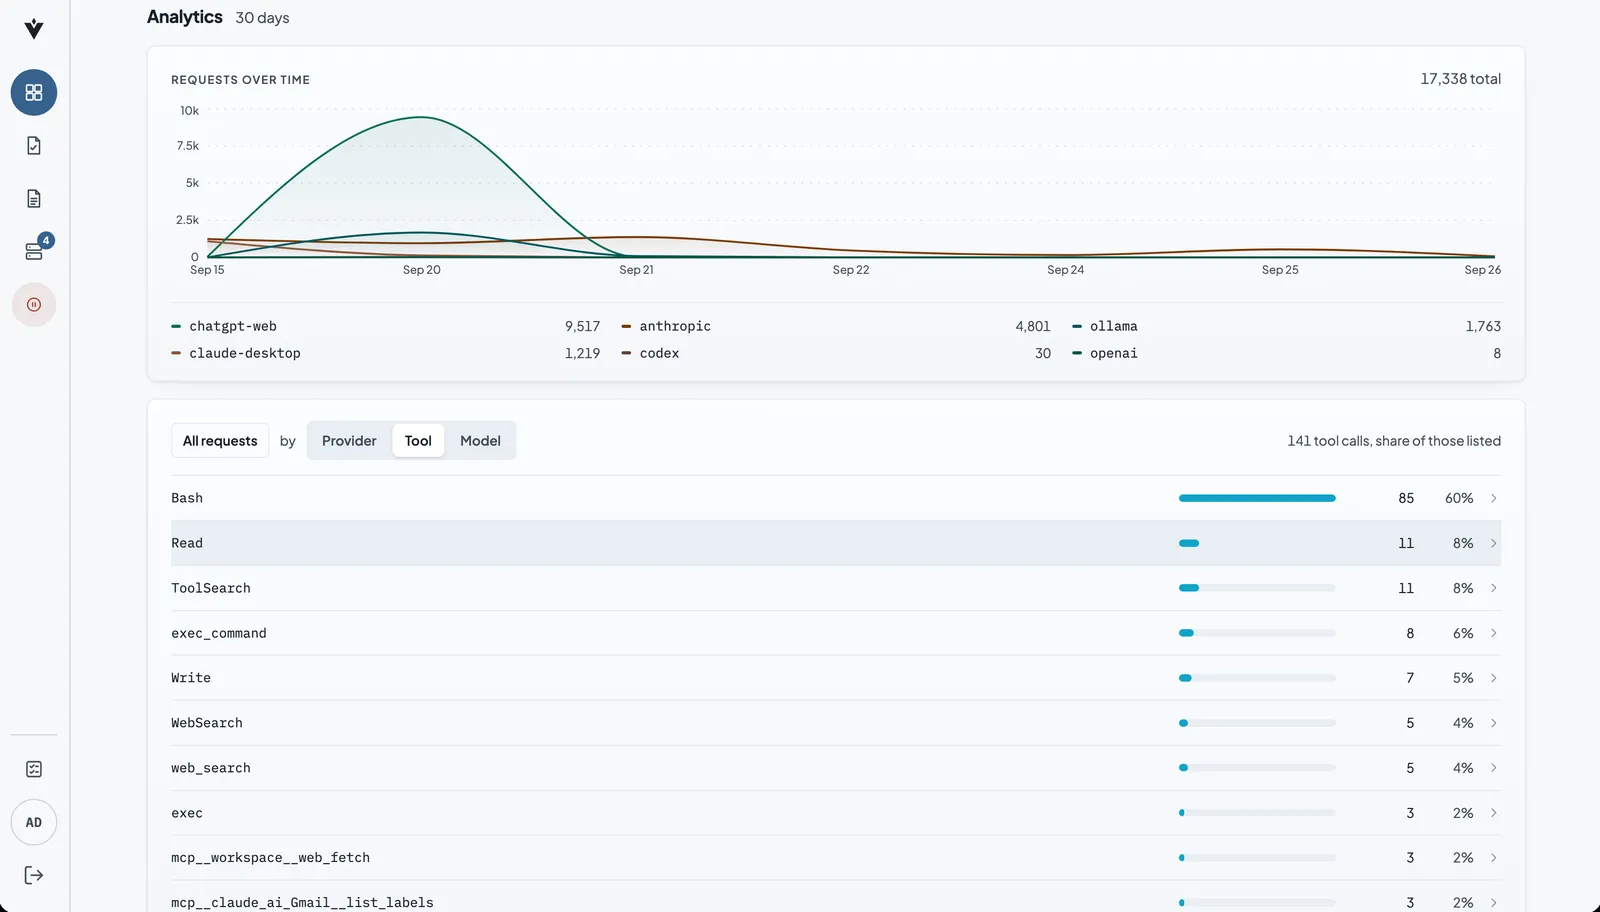
| The console | Self-hosted. Policy, fleet health and every decision in one place you run. |
| Install | On macOS, a signed package with no plugins and no SDKs. Nothing changes for your people until a request is not allowed. |
| What it is not | Not a monitoring dashboard, a cloud gateway, a wrapper around your tools or a model vendor. |
Questions about enforcing AI policy on the device
How is AI policy enforced on the device?
A checkpoint on each enrolled device rules every captured request against the policy you declared, before a prompt leaves or a command runs. Values your policy flags are screened before the prompt leaves, on a best-effort basis. On the Anthropic API format that Claude Code uses, a tool call your policy refuses never runs; other governed providers are captured and sealed.
Why decide on the device and not in the cloud?
Telemetry shipped to the cloud and correlated later, and written policy alone, share one blind spot: neither is present at the moment an action runs. Deciding where the person works closes that gap, the sealed record lands on a server you run, and governed providers receive only what your policy let out.
Does Verillian receive our data?
No. The console and the record run on your own infrastructure, under a key only you hold. Verillian collects nothing for itself and never receives a copy.
Which frameworks is Verillian aligned to?
CJIS Security Policy v6.1, HIPAA, NIST 800-53 and CMMC. Aligned, not certified: your assessor decides what satisfies your controls.
Watch one request decided on your own device
Bring a request from your own work and see it ruled and recorded live.