Security questionnaire answers.
Short, exact answers to the questions a security review asks first: who holds the keys, where the data lives, what the agreements cover and how it runs day to day.
Who holds the keys
| Topic | Answer |
|---|---|
| The keys are yours | Audit content is encrypted under a key your institution generates and holds. Opening the record takes that private key, which never reaches us, and the exact algorithms are written up in the security model for your cryptographer to check. |
| Each device signs with its own key | Each captured interaction is signed with a key minted for that device at enrollment and delivered to it once. The admin server keeps only the public key, so it can verify a signature but holds no copy of the key to sign with. |
| Custody, rotation, and recovery sit with you | Because the keys are yours, generation, custody, rotation, and recovery are yours too. We give your security team the operational guidance for running them in your own deployment. |
| There's nothing on our side to subpoena | If a legal demand reaches us, we couldn't act on it if we tried. The server isn't ours and we can't log into it, so we never get past the first hurdle. Even if we did, the content is sealed under a key we never held. |
Where your data lives
| Topic | Answer |
|---|---|
| Your deployment stays in your environment | The checkpoint, the admin server, and the sealed record all run on infrastructure you operate. Your prompts, responses, and tool calls are never sent to us, from any deployment, for any reason. |
| Our own corporate data is US-based | The limited business-contact and website data we do hold is processed by US-based providers, and we'll share the current provider list with your review on request. |
Attestation, DPA and BAA
| Topic | Answer |
|---|---|
| SOC 2 and third-party attestation | We don't hold a SOC 2 attestation yet, and we'd rather tell you that than imply otherwise. Self-hosting narrows what an attestation would cover, since your sensitive data never passes through us, and when we hold one, this page will say so. |
| Data processing addendum (DPA) | If your institution needs a DPA, a draft is ready for your counsel's review today, and it's finalized with you before signature. Your deployment data never flows to us, so the processing it governs is limited to business-contact information. |
| Business associate agreement (BAA) | We never receive protected health information from your deployment, so under the self-hosted model you may not need a BAA at all. If your counsel wants one anyway, a draft is available for review on request. |
Availability, support and incidents
| Topic | Answer |
|---|---|
| Your control doesn't depend on us | Policy enforcement and audit capture run on your infrastructure with no Verillian service in the request path, so your control keeps working even when we don't. The status page explains why our uptime isn't your problem. |
| Support and service levels | Support tiers, response targets, and our update commitments live in your agreement, and we'll walk your procurement team through the current terms before you sign anything. |
| Updates and patches | We publish security updates for the checkpoint and the admin server, and you apply them on your own schedule, inside your own change process. |
| Security incidents | If an incident affects data we hold, we notify affected institutions without undue delay. Because your deployment data stays with you, an incident on our side can't expose data we never had: your prompts, your responses, and your record stay where they live, with you. |
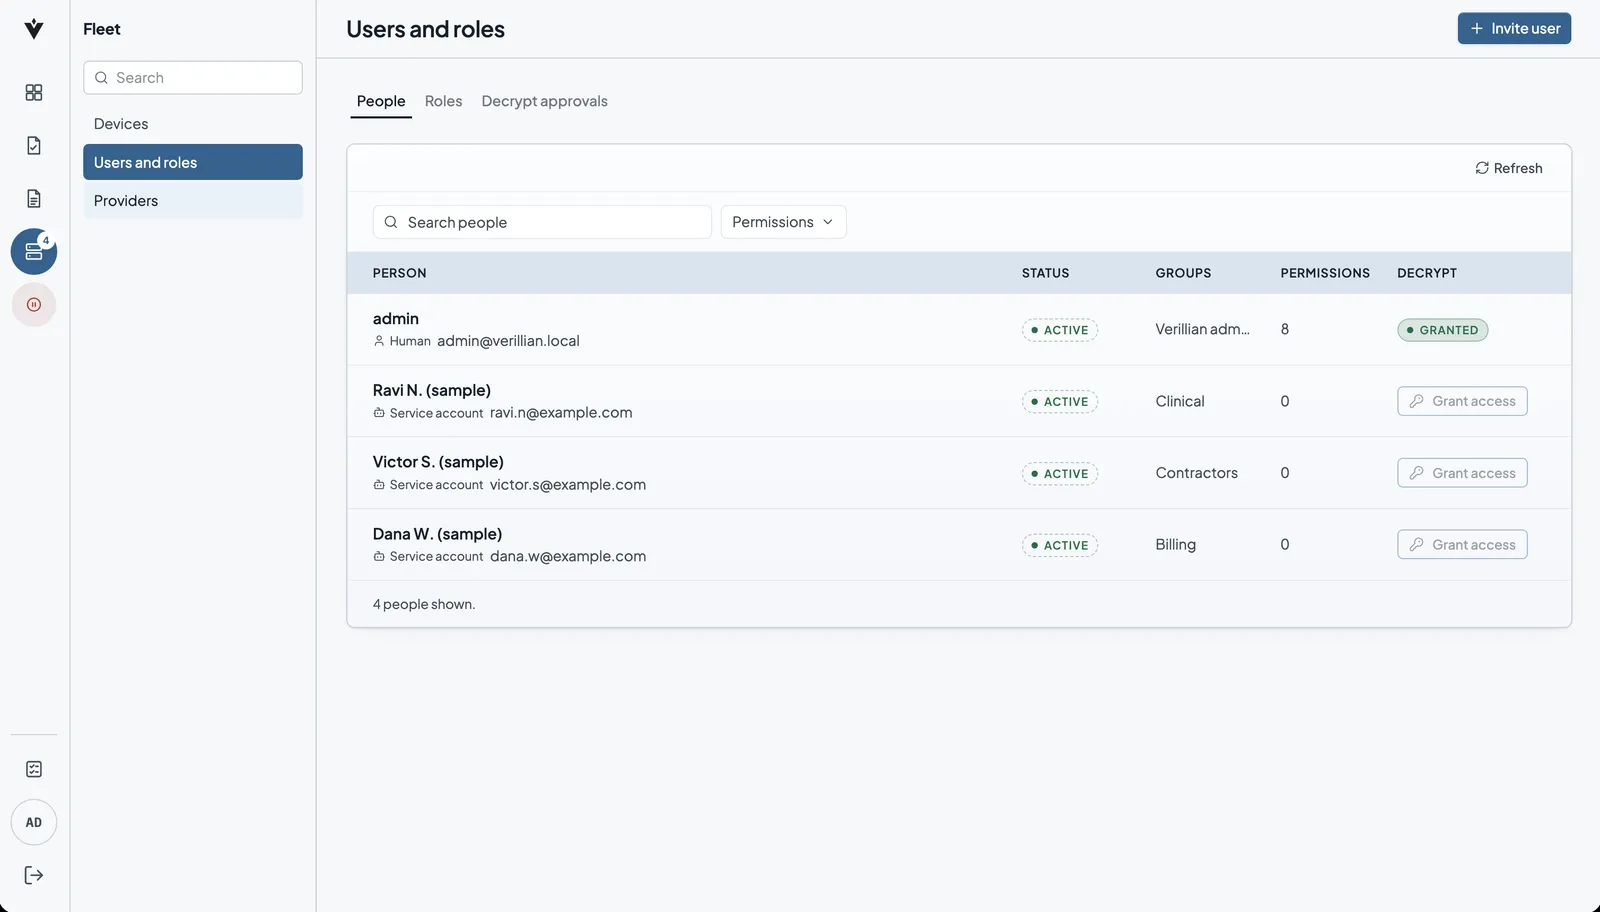
Who can open a record
Roles and groups decide who can decrypt content, with your key.
PDFArchitecture and data flowFollow a request from the device, through the ruling, into the sealed record, with what crosses each boundary marked.PDFTrust and security overviewThe one document to attach to a security questionnaire: posture, keys, and data flow in a single read.PDFThe full security modelThe six properties enforced by construction, from on-device decisions to key isolation, with what each one buys your review.PDFCompliance mappingsFramework by framework, what Verillian lines up with, and the control-by-control detail on request.
See your policy decide on a real device
Book thirty minutes, bring one of your own requests, and watch it ruled live.